Automation should not mean giving up control.
Define who can access what, which actions run automatically, which require approval, and what gets recorded.
Access and automation are configured around your systems, permissions, governance, and operating requirements.
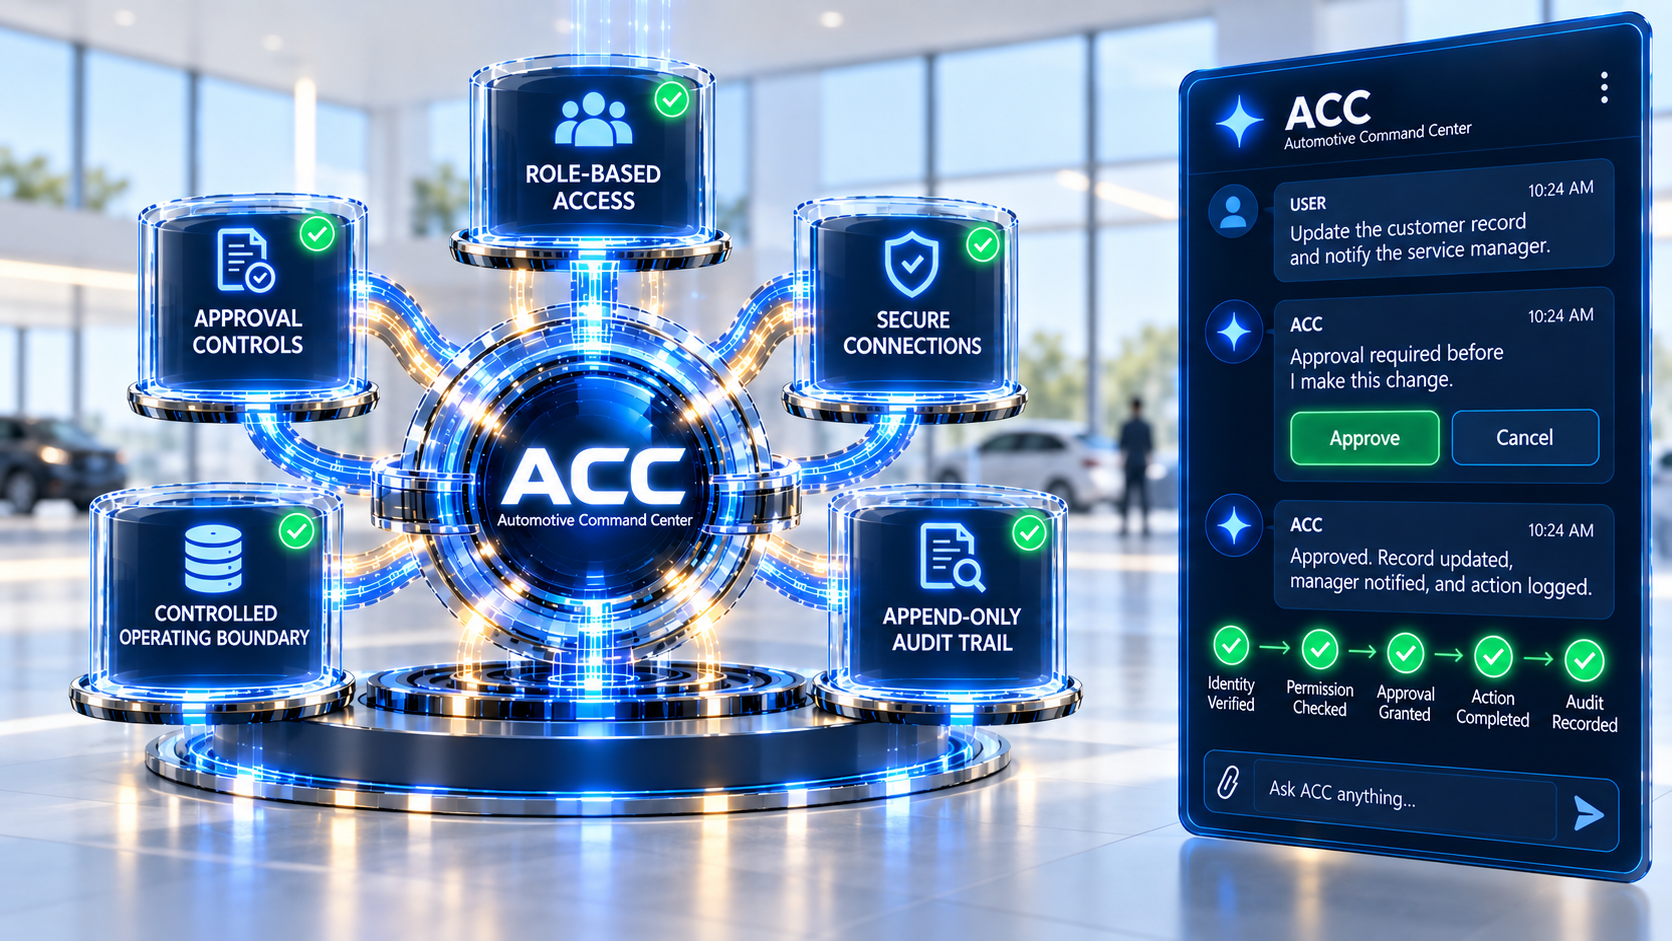
Illustrative view of role-based access, approval controls, and append-only action history.
Every action starts with knowing who is asking.
ACC should not treat every employee the same. A request passes through identity, role, permissions, and workflow rules before anything runs.
- REQUEST
- IDENTITY
- ROLE
- PERMISSION
- WORKFLOW RULE
- ACC
POLICY CHECKS BEFORE EXECUTION
- 1ACCESS POLICYIs this user allowed to request the action?
- 2SYSTEM POLICYDoes the connected platform permit this operation?
- 3WORKFLOW POLICYIs this action allowed to execute automatically?
- 4APPROVAL POLICYDoes an authorized person need to approve it first?
A single store may use simple department-level permissions. A group can apply broader policy by rooftop, region, role, and workflow. Dealer Group Governance.
The user sees Chat. ACC checks the controls underneath.
Access and automation are configured around your rules.
ACC can read, prepare, and act within the access and controls approved for the deployment. Deployment scope is defined by your organization.
READ
Retrieve approved information.
PREPARE
Assemble reports, exceptions, recommendations, or proposed changes.
ACT
Perform approved actions where access and permissions allow.
Approval required before I make this change.
This demonstration simulates approval and execution; it does not access dealership systems.
Approval rules may vary by:
- role
- workflow
- rooftop
- action type
See what happened after the automation runs.
- 8:14 AMLead follow-up workflow startedWorkflow
- 8:14 AMUser identity verifiedACC
- 8:14 AMCRM read completedCRM
- 8:15 AMFollow-up action approvedManager
- 8:15 AMCustomer record updatedCRM
- 8:15 AMWorkflow result returned through ChatACC
This append-only audit history can show:
- who initiated
- what ran
- which systems were involved
- whether approval occurred
- what result was returned
Your data should work inside the environment your organization approves.
LotLight ACC is built on L2H.ai's Agentic Command Center platform, which provides the underlying workflow, governance, integration, and control architecture.
Architecture and controls are designed and documented to support enterprise security requirements. Framework mappings and current assurance documentation can be reviewed during the security process.
Your data. Your workflows. Your rules.
See how ACC can automate without giving up control.
Bring us one workflow and the rules around it. We will map where ACC reads, where it acts, where approval belongs, and what gets recorded.